Chaitanya Gunupudi | IT Senior Engineer & Independent Researcher
University of Maryland
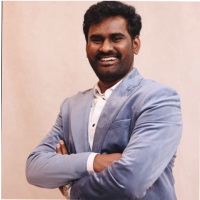
Chaitanya Gunupudi is a Senior Cloud Platform Engineer and AI Research Practitioner at the University of Maryland, specializing in enterprise AI infrastructure, identity and access management, cybersecurity, and cloud-native systems. He builds and operates AI platforms and certificate automation infrastructure deployed across large-scale research and education environments, with a focus on HIPAA and FERPA compliance, zero-trust architecture, and federated identity systems. His research spans AI-driven cybersecurity, intelligent clinical decision support, and federated AI infrastructure, with peer-reviewed publications in IEEE and international journals, and filed patents in AI-driven systems and security architecture. He is an accepted speaker at EDUCAUSE Annual Conference 2026, Internet2 Technology Exchange 2026, BrainStorm Poconos 2026, and the Coalition for Networked Information, and serves on the Technical Program Committees for IEEE Cluster 2026 and IEEE Big Data 2026. A Research Group Member of the Centre for AI and Digital Policy spanning over 130 countries, he is currently a doctoral candidate researching AI systems and large language models at Harrisburg University. He holds a Master of Science in Cybersecurity from the University of Maryland, and certifications including AWS Certified Solutions Architect and Oracle AI Agent Studio Foundations Associate.
Appearances:
Identity Week America - Day 2 @ 15:00
From manual chaos to autonomous identity: AI-driven certificate lifecycle management at scale and the post-quantum deadline every IAM team is already behind on
Identity infrastructure fails quietly certificates expire, domains go dark, and helpdesks flood and most organizations are managing this with manual processes that cannot scale. This session is a practitioner's account of deploying AI-driven certificate lifecycle automation across 8,707 TLS certificates, 153 domains, and 39 departments serving 40,000+ users, achieving a 64% reduction in helpdesk tickets and zero certificate-related outages since deployment. But the harder conversation is what comes next: Executive Order 14412 (June 2026) has mandated migration to post-quantum cryptography, NIST FIPS 203, 204, and 205 are finalized, and every RSA and ECC certificate underpinning your federated identity, TLS, and PKI-based authentication is now on a compliance clock. This session covers how AI automation transforms certificate operations from a human-error problem into a governed, auditable system, what crypto-agile architecture looks like in a live multi-domain production environment, and why AI-driven certificate management is the only operationally realistic path to post-quantum migration at scale built from lessons learned running it in production, not in a lab.
GET INVOLVED AT IDENTITY WEEK AMERICA
Created by
Terrapinn is proud to be a member of isla.
Working together to build sustainable events